

I have a standing rant about password security for small businesses. If you have sat in a meeting with me for more than twenty minutes, you have probably heard some version of it. Denmark just gave me the best opening line I’ve had in years.
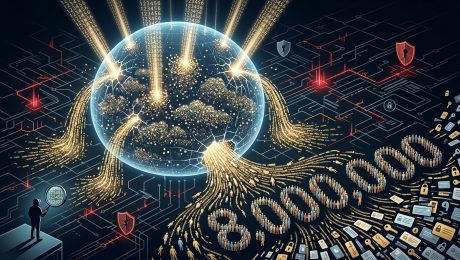
Earlier this month, the Danish government confirmed that someone got into its Central Register of Persons, the national database that holds the core identity record for nearly every resident. The attacker accessed information on 8.8 million people. The person claiming responsibility says they got in through an account at a small IT company with legitimate access to the registry, and that account’s password was “123456.” Danish newspaper Politiken reported that at least three of the company’s accounts used that same password, including an administrator account.
How a six-digit password reached 8.8 million records
The details are worth a minute of your time. According to documents reported by Danish broadcaster TV 2, the attacker first logged in on September 10 and ran roughly 14 million automated searches over the next ten days. Nobody noticed until October 2.
I keep coming back to how they finally caught it. No security tool flagged it. A staffer at the ministry noticed an invoice showing unusually high activity from the vendor’s account. Someone read a bill.
That vendor, a company called Pays ApS, was authorized to use the registry to validate business customers’ records. Its managing director has confirmed the company’s access was exploited. A small firm held the key to something enormous, and it protected that key with the first six digits on the keyboard.
If you run a professional services firm, that arrangement should feel uncomfortably familiar.
Convenience wins the first round almost every time
I don’t think anyone at that company is stupid. I think someone set up a handful of accounts, needed several people to get into them, picked something everyone could remember, and told themselves they would fix it later. Later never came. I see the same pattern in firms of 50 people and firms of 150.
Humans pick convenience over security by default. Security takes effort, and effort loses to a filing deadline every single time. One weak password is a mistake. Three accounts sharing it, one of them with administrator rights, is a habit, and habits are exactly what attackers count on.
The shared admin password usually exists because sharing access is a real problem. The seasonal hire needs access to the client portal. The office manager needs access to the vendor account while the partner is on vacation. Nobody wants to be the bottleneck for a two-factor code at 8 p.m., so the fix has to make sharing safe. Pretending people won’t share has never worked.
Your vendors hold keys to your data too.
Denmark’s breach did not start inside the government. It started at a vendor. That is the part I want every CFO and managing partner to sit with for a minute.
Verizon’s 2025 Data Breach Investigations Report found that third-party involvement in breaches doubled to 30 percent, while credential abuse remained a leading way attackers got in at 22 percent. Your firm’s data does not just live on your own servers. It lives with your practice management software, your document portal, your payroll provider, and, yes, your IT company. That includes us.
Every one of those relationships involves accounts that someone, somewhere, protects with a password. You are allowed to ask how. Good vendors will answer without getting defensive. A vendor that gets cagey about it has told you something important.
What we do about shared passwords at C2
We have the same sharing problem every firm has, multiplied by every client account we manage. Our answer is a password manager. We use Keeper, which lets us share credentials across the team and attach the second factor to them. In practice, a technician can access the account they need without me texting a password, and without anyone chasing me for a two-factor code.
Every admin account gets its own unique password and multifactor authentication. When someone leaves, their access leaves with them, and we never have to wonder which sticky note they saw. We also want to hear about strange activity long before an invoice arrives. Fourteen million searches should set off an alarm somewhere other than accounts payable.
None of this is exotic. It is the same tooling large companies use, at a price that makes sense for a 75-person firm. Small businesses deserve that, and frankly, so do the people whose records they hold.
One question to ask this week
Send one email to your IT provider and one to the vendor that holds your most sensitive client data. Ask them this: “Does any account with access to our data share a password with another account?”
Suppose the answer comes back fast and clear, great. If it takes a week and a pile of meetings, you have your answer.
A three person research team broke into OpenAI last month. They used Anthropic’s Claude to do it, and the entire operation took less than 72 hours. (TechCrunch, The Register) It was a legitimate bug bounty exercise, fully authorized, and OpenAI paid the team $6,500 for finding the holes. Nobody stole anything. That part of the story isn’t actually what should worry you.
I read the headline the same way most people probably did, half expecting a genuine attack, and had to go back and read the actual reporting to understand what happened. It turned out to be closer to a stress test than a heist. That distinction matters. So does the speed at which it happened, and that’s the part I don’t think is getting enough attention.
What Happened
The researchers, a small security firm called Hacktron AI, found a vulnerability in the software running OpenAI’s public community forum. They used Claude Opus 4.8 to try building an exploit and got stuck on a security feature that blocked the attack. A day later, Anthropic released Claude Opus 5. The team switched models, and the new version cleared the exact hurdle that had stopped the old one. From there they took over an OpenAI employee’s account, reached the company’s private code repository, proved it with a harmless pull request, and reported everything before touching anything sensitive. OpenAI patched the holes within 14 hours.
The Part That Worries Me
What stops me isn’t that a security team found a flaw. Security teams find flaws every week, that’s the job. What stops me is the 24 hours between a model failing at a task and the next version of that same model succeeding at it. Whatever assumptions your firm made about what AI can or can’t do six months ago, some of them are already wrong, and the gap keeps shrinking.
I’ve said some version of this before: AI is not magic, and it’s only as good as the intent and oversight behind it. That part is still true. What’s changed is how fast the distance between “can’t” and “can” closes, and most businesses, mine included, are not built to reevaluate that distance every quarter.
Nobody’s Incentivized to Slow This Down
Here’s my honest, entirely unqualified read on why the conversation about slowing down never seems to land anywhere. I’m not an economist, and I could be wrong about this. But the companies building these tools are run by genuinely smart engineers, who then hire genuinely smart finance people, and finance people are paid to maximize growth, not to install brakes. Regulation is one of the only real mechanisms that rewards restraint when competitors have none. Right now, the labs at the frontier have more to gain by shaping that regulation on their own terms than by slowing down and waiting for someone else to write it for them.
I don’t think that’s a conspiracy so much as it’s just how the incentives line up. Nobody in a position to say “maybe we should all move slower” has much to gain from being the one who says it first.
What This Means if You Run a Business
None of this is a reason to avoid AI. I’ve told clients for years that flying into AI expecting it to magically cut costs and eliminate half your staff is how you end up disappointed, not transformed. The tools genuinely work well on specific, well-scoped problems. They work considerably less well as a general answer to “we should probably be using AI for something.”
What I’d ask, if I were running a professional services firm this week, is whether anyone at your company has written down what your AI tools are allowed to touch, who checks the output, and what happens when something goes wrong. Not whether the AI itself can be trusted. Whether the people who deployed it built any guardrails around it before they turned it loose.
The researchers who got into OpenAI did it as an authorized test, reported everything, and got paid for their trouble. The next team that finds a gap like that one might not be nearly as polite. Pick one AI tool your firm is already using and ask exactly who is responsible for it. If nobody has a clean answer, that’s this week’s project.
Quick and Easy: A security team broke into OpenAI using Claude in under 72 hours, and it was authorized research, not an attack. The real story is how fast AI capability jumped between model versions, not the breach itself. If your firm uses AI tools, write down what they can touch, who checks their output, and who is responsible when something goes wrong.
A few weeks ago, my team spent a meeting arguing about whether AI should ever be the first voice a client hears when something breaks. We didn’t fully agree, and I think that disagreement is worth more to you than a tidy answer would have been.
Where AI Helps
Voice AI has gotten good enough that it’s mostly stopped being annoying, which is a bigger deal than it sounds. Someone on my team described calling her pharmacy recently and getting routed by a system that actually understood “I have a problem with my foot and need to talk to the doctor,” and got her there without the usual maze of numbered menus. That’s a real shift from the chatbot era, when the whole point of the experience seemed to be making you beg for a human before it finally gave up and connected you.
There’s a real case for using something like that on simple, well-defined requests: resetting a password, answering a basic account question, routing a call to the right person faster than a receptionist juggling four lines, that kind of thing. People are getting more comfortable with it too, the more they run into versions that actually work on the first try.
Where We Draw the Line
This is what stopped us from just rolling it out. To answer even a simple question like “I forgot my password,” an AI system needs some level of access to our password management tools and parts of our clients’ network security. That’s not a small ask. We manage the systems that protect law firms, accounting practices, and property managers for a living, and handing any part of that access to a system we can’t fully audit in real time isn’t a convenience trade we’re willing to make yet.
There’s a simpler truth underneath it all, too. When someone’s technology breaks, the last thing they want to talk to is more technology. They want a person who understands what’s actually going on and can tell them, in plain language, what happens next. That’s not a preference we’re trying to design around. It’s the job.
This isn’t just a customer experience question either. Many of our clients deal with compliance requirements around who can access what, and when. An AI system sitting between a client and their own account access needs the same audit trail a human technician would need: a clear record of what it looked at, what it changed, and who is accountable if something goes wrong. Most of the AI support tools I’ve looked at aren’t built with that level of accountability in mind yet, because speed and convenience were the selling point, not oversight.
The Real Question Isn’t Whether AI Can Do It
The honest version of this decision isn’t “can AI handle support calls.” Some of it, clearly, it can. The real question is what you’re willing to hand over for that convenience, and whether the people on the other end of the call get an actual choice. My own answer, for now, is that anyone who calls us gets a real person. If we ever build in an AI option down the line, it will be exactly that: an option, clearly labeled, with a human always one step behind it.
If your own firm is weighing something similar, whether it’s a phone system, a chatbot, or anything that touches client data, ask the vendor pitching it one specific question: what does this thing have access to, and who is watching what it does with that access? If they can’t answer clearly, you already have your answer too.
Quick and Easy: AI voice systems have gotten good enough to genuinely help with simple requests like password resets and call routing. The trade off is access, since even basic AI support usually needs some reach into account and security systems. Before adopting one, ask exactly what it can touch and who is accountable for it.
Every law firm I walk into for the first time has the same blind spot. They know exactly how their document management software works, right down to which folder holds which matter, and they have never once asked what happens to that traffic once it leaves the building.
Small business network security is not about buying one good piece of hardware and calling it finished. It is a handful of separate layers working together, and most firms I inherit from a previous vendor are missing at least two of them.
What Small Business Network Security Covers
A firewall controls what gets in and out at the edge of your network, which is the piece most people picture when they hear the term. Segmentation keeps a compromised laptop in the front office from reaching the server holding your client files. Monitoring watches what’s happening on the network in real time, instead of assuming the firewall caught everything. Patching keeps every piece of software from carrying known holes that were fixed months ago but never installed.
Firewall Setup Services Are a Start, Not a Finish
A firewall is the locked front door of the building, and a locked front door does little if every window is wide open and nobody checks who is still inside after hours. I still run into firms with a firewall installed a decade ago, left on factory settings, and never touched since. That configuration matters more than the brand on the box, and it needs a real review at least once a year as your firm’s tools and staff change.
Firewall setup services worth paying for include tuning the rules to your firm’s specific traffic, not just plugging in a device and walking away. I have replaced more misconfigured firewalls than blank ones over the years, because a firewall installed wrong gives a false sense of security that is worse than knowing you have a gap.
Network Monitoring Service: Why Watching Matters as Much as Blocking
Blocking known threats at the edge stops the obvious attacks, but the ones that hurt firms are rarely obvious on day one. A network monitoring service watches traffic patterns and flags behavior that looks wrong even when nothing has technically been blocked yet, like a workstation suddenly talking to a server it has never contacted before. Catching that in the first hour is the difference between an incident and a headline. Most firms without monitoring don’t find out something happened until weeks later, usually when a client calls about a strange email.
Wireless Networks Are Part of This Too
Guest wifi that shares the same network as your accounting software is a common gap I find on a first visit. It feels harmless, since it is just for visitors checking email in the lobby, until someone realizes that network can see the same file shares as everyone else in the building. Separating guest wifi from your actual business network takes an afternoon to configure correctly, and it closes a door most firms never realized was open.
Remote Access Without Opening the Whole Network
Hybrid work turned VPN configuration into something firms have to think about, because half your staff might be working from a home network with problems your office network doesn’t share. A properly configured VPN gives remote staff access to exactly what they need without handing every device on their home network a path into your servers. I have inherited VPN setups that worked technically but were configured so loosely that a compromised home router became a direct line into a law firm’s case files.
Patching Is Boring, Which Is Exactly Why It Gets Skipped
A missed patch on a piece of network equipment sitting quietly in a closet does not announce itself the way a broken printer does, so it can sit vulnerable for months without anyone noticing. Automating that process, rather than relying on someone remembering to check, closes one of the most common gaps I find during a first assessment. It is not an exciting fix, but most of the real fixes are not.
Why Professional Services Firms Need a Different Plan
Professional services firms carry a specific kind of risk that a generic small business network plan does not account for. An accounting firm’s network needs to assume client tax data will move through it at volumes the rest of the year never sees, concentrated into about six weeks. A law firm’s needs assume privileged documents are what’s most worth protecting, not just network uptime. Building the same plan for a retail shop and a law office misses what matters to each one.
What This Looks Like for a Fifty-Person Accounting Firm
A firm that size typically needs a properly configured firewall at the edge, a separate network segment for guest and personal devices so they cannot reach the accounting software, monitoring that alerts a real person rather than filling a log nobody reads, and a patching schedule that does not depend on someone remembering to do it manually. None of this needs to be complicated or expensive to be effective. The complexity mostly comes from vendors selling features a fifty-person firm will never use.
None of this needs to happen all at once, and I do not recommend trying. Firms that attempt every layer in a single month usually burn out their staff’s patience for change and end up rolling half of it back. A phased approach – firewall and segmentation first, monitoring and VPN cleanup second, patch automation third – gets a firm to a genuinely secure place without disrupting a normal work week.
If nobody has looked at your network setup in the last year, that is worth fixing before your next busy season, not after an incident forces the conversation. Ask whoever manages your network right now to walk you through exactly what happens after something gets past the firewall. If the answer is vague, that is your actual gap. If so, let’s talk.
The phishing email that gave itself away with a typo and a logo in the wrong shade of blue does not exist anymore, at least not the ones causing real damage. AI writes cleaner English than most of the people it is trying to fool, and that single fact has changed what phishing prevention for businesses requires.
I have been doing this long enough to remember when spotting a phishing email took about ten minutes of training, mostly checking the sender address and glancing at the logo to see if it looked slightly off. None of that holds up reliably anymore.
What Changed
A large language model can write a flawless email in the exact tone of your firm’s biggest client, because it was trained on millions of real emails that already sound exactly like that. It can pull someone’s actual name, title, and recent activity into a message that reads like it came from a person who genuinely knows them. There is no broken translation anywhere in the process anymore, so none of the old tells apply.
Voice cloning takes a few seconds of audio, sometimes lifted straight from a firm’s own promotional video, and turns it into a convincing phone call. I have talked to colleagues in this industry who have had a client call in a panic because they got a voicemail that sounded exactly like their managing partner asking for an urgent wire transfer. It was not their managing partner.
Video is not far behind the voice. A convincing deepfake used to require real production time and a decent budget, and a few minutes of footage from a firm’s own website or a conference recording is often enough now. I do not expect video calls to become an unreliable way to verify identity within the next year or two, but firms need to plan for that shift now rather than after it happens to them.
Why Professional Services Firms Are a Better Target Than Ever
Law firms move money for real estate closings and accounting firms move client funds during tax season. Property management firms process rent and vendor payments every single month on top of that. All three run on the same vulnerability: a wire transfer or an ACH request that is one convincing email away from becoming someone else’s payday.
Real estate closing fraud has been a known problem in this industry for years, well before AI made the emails better written. A buyer gets a message that looks exactly like it came from the title company, with wiring instructions changed at the last minute. AI mostly made the email itself harder to catch, which means the same old scam now clears the one filter, sloppy writing, that used to catch a meaningful share of these attempts.
I have watched this play out with a property management client of mine. Someone emailed posing as a tenant, asking to redirect a security deposit refund to a new bank account, and used the tenant’s actual name along with a real unit number pulled from a public rental listing. Our procedure caught it because nobody moves money at that firm without a callback first, but the email itself would have fooled almost anyone reading quickly.
The old advice to trust but verify assumed you could verify by picking up the phone and recognizing a voice. That assumption does not hold anymore, and firms still operating on it are exactly the ones an AI-generated phishing attempt is counting on catching off guard.
Cybersecurity Training for Employees Has to Change Too
Most cybersecurity training for employees still teaches pattern recognition on artifacts that no longer reliably exist. People get trained to spot a bad logo or a misspelled domain, then walk straight past a message that has neither, because the person who wrote it didn’tt make either mistake. Security awareness training in 2026 has to teach a different skill entirely: pausing on urgency itself, regardless of how polished the message looks.
I tell clients the goal is not to become suspicious of every single email. That is exhausting, and nobody sustains it for more than a week. The actual goal is one specific habit around money and access requests: if it involves moving funds or changing account details, verify it through a channel you already know is real before doing anything else.
What This Looks Like in Practice
A callback procedure on a phone number you already have on file, not one provided in the email or voicemail asking for money, stops most of this cold. Dual sign-off on any wire transfer or account change removes the single point of failure that one tired employee represents on a busy Friday afternoon. Multi-factor authentication on every account closes the door that a cloned voice or a well-written email can’t open by itself.
None of this requires new technology most firms do not already have access to. It requires deciding, in writing, what your firm’s actual verification procedure is before you need it, not while someone is on the phone pretending to be your managing partner.
None of this is really new, either. Technology built by humans has always failed in predictable ways once the incentive gets big enough, and I have been saying some version of that for longer than AI has existed. What changed is how good the disguise looks. The underlying con is the same one it always was.
The firms that hold up are not the ones with the fanciest security software. They are the ones who built one boring, repeatable habit around verifying anything involving money, and stuck to it. Pick one financial process at your firm this week – wire transfers, vendor payments, whatever moves the most money – and write down exactly how your team is supposed to verify a request before acting on it.
If you need help with training or have questions surrounding this issue, let’s talk.
Small businesses don’t get targeted by ransomware because they’re interesting. They get targeted because they’re profitable and poorly defended, and attackers do the math the same way any business does.
I’ve said this to clients for years, and I still watch the same disbelief cross their faces. Nobody wants to think a fifty-person accounting firm in Southern California is worth an attacker’s time. The numbers say otherwise, and they’ve been saying so for a while now.
The Numbers Behind Small Business Ransomware Protection
80% of small and midsize business breaches now involve ransomware, compared to 39% at large enterprises, according to Verizon’s 2025 Data Breach Investigations Report. That difference isn’t random. Larger companies have dedicated security staff, segmented networks, and faster patching. Most small firms have neither the headcount nor the budget for either one, and attackers know it.
Professional services firms specifically, law offices, accounting practices, and consulting firms, became one of the most heavily targeted sectors in ransomware data from the recovery firm Coveware. That tracks with what I see. These firms hold exactly what a ransomware operator wants: clients’ financial records, case files, personal data, and businesses that can’t afford to stay offline during tax season or a court deadline.
It’s Not Personal, and That’s the Point
I tell clients it used to feel personal. Some kid in a basement decides to mess with your business specifically. That’s mostly gone. Now it’s closer to pollution. It’s always pressing in from the outside, looking for a weak point, with no interest in who you are specifically. It just needs one person to click one link, because sending a million emails costs almost nothing and only one has to land.
That shift matters because it changes what “not a target” truly means. Nobody is deciding your firm doesn’t matter enough to attack. Nobody is deciding anything about your firm at all until the attack already worked.
I’ve had clients tell me their business is too boring to bother with, that they don’t have anything a criminal would want. I remind them that a ransomware operator doesn’t care what the business does. They care whether the firm can pay to retrieve its files and whether its defenses are weak enough to be worth the effort. A fifty-person accounting firm during tax season checks both boxes better than almost any target I can think of.
What Reduces Risk
Multi-factor authentication on every account, not just email, closes the door that stolen credentials alone used to open. It’s the single control I push hardest on, because it stops the most common way attackers get in with the least disruption to how your team works.
Endpoint security solutions that actively monitor and respond, not just antivirus software that scans on a schedule, catch the behavior of an attack in progress instead of waiting to recognize a known virus signature. The difference matters because most modern ransomware doesn’t look like the viruses that older antivirus tools were built to catch.
Backups that are tested, not just scheduled, are the difference between a bad week and a business-ending event. I’ve seen firms discover their backups had been silently failing for months, and they only found out during the one week they actually needed to restore something.
Incident response support, meaning an actual written plan for the first hour after something goes wrong, matters more than most firms expect. The firms that recover fastest aren’t the ones with the most expensive tools. They’re the ones who already know who to call, what to shut down first, and who’s authorized to make that call at two in the morning.
What This Costs vs. What an Attack Costs
Every one of these measures costs money and a little bit of friction for your staff. I won’t pretend MFA prompts are fun or that anyone enjoys a tabletop exercise for an incident that hasn’t happened yet.
Weigh that against a ransomware event that takes your firm offline during a filing deadline, a court date, or tax season, and the math stops being close. Most firms that get hit spend more recovering from a single incident than they would have spent on prevention for several years.
If you don’t know where your firm currently stands on any of this, that’s the actual starting point, not buying more software. Start with an honest look at your multi-factor authentication coverage, your backup testing, and whether anyone in your office could answer “what do we do first” if a ransomware alert went off tomorrow.
I walk into a room, and things start working. It happens often enough that my clients have started joking about it, like I’m carrying some kind of charm. I don’t think that’s what’s actually going on. More likely, the equipment was already failing quietly, and I’m just the one who finally noticed.
This came up in a conversation with a colleague around my age, who told me he missed the days when Outlook just worked properly. I asked him to actually think back and tell me what year that was. He got quiet for a second, then admitted it was around 2006. Twenty years felt like yesterday to both of us, which tells you something about how we experience time, but it also missed a bigger point. Outlook has real problems today. The difference is that almost everything else does too, and that isn’t in our heads.
Why Reliability Declined
For a stretch of time around the pandemic, the semiconductor industry took a series of direct hits. In February 2021, a severe winter storm cut power across Texas and forced major chip plants, including facilities run by Samsung and NXP, to shut down for weeks. Forbes covered the disruption in detail as it was unfolding, and the effects rippled outward for years afterward, showing up in everything from laptops to cars.
Manufacturers never fully rebuilt that lost capacity before demand for computers and phones spiked further. On top of that, plenty of companies responded to rising costs by trimming quality wherever customers were least likely to notice right away. A laptop that used to last five years might now last three. A router that once ran quietly in a closet for a decade now needs replacing much sooner. None of this is a conspiracy. It’s a straightforward response to real supply problems, and it happened right as more of our lives moved onto these devices than ever before.
What This Means for You
If your equipment is failing more often than it used to, it probably isn’t because someone in your office is doing something wrong. The hardware itself likely isn’t built to the standard you remember, and that standard isn’t coming back on its own.
The response to that isn’t nostalgia. It’s planning around it. Replace hardware on a schedule instead of waiting for it to die, and treat backups as a routine part of doing business rather than something you scramble for after a crisis. A three- to four-year replacement cycle for laptops and a firm habit of testing your backups, not just running them, will save you more grief than any amount of wishing your equipment behaved the way it did a decade ago. A firm that expects a piece of equipment to eventually fail, and plans for it, loses an afternoon. A firm that assumes everything will keep running the way it did in 2015 loses a great deal more than that.
I still get called in, and things start working again, and I still let the joke about being some kind of charm ride, because it’s funnier than the real explanation. The real explanation is aging equipment paired with a supply chain that still hasn’t fully recovered from a rough couple of years. None of that is mysterious, and none of it is going away on its own, so the businesses doing best right now are the ones planning around it instead of being surprised by it every time.
If your team hasn’t looked at when your hardware was actually purchased, not when it feels like you bought it, that’s a good place to start before your next refresh.
A few years ago, one of my technicians got cornered by a client asking why their internet always seemed to just work. My colleague told her it was the jack fairy. She meant me.
I think about that a lot, because it gets at something people almost never notice about good IT support. When everything works, nobody thinks about how. The internet flows out of the wall, the printer talks to the copier, the phone rings when it’s supposed to. Nobody sees the effort behind any of it. They just see the result, and the result looks like magic.
The Alarm Nobody Could Find
Not long ago, I got called to a client’s office because an alarm was going off and nobody could tell where it was coming from. The only person in the building that day wasn’t a “tech person,” and she didn’t need to be for her job. She took pictures on her phone, trying to describe the sound to me over the phone, and I could hear her starting to panic. I told her I’d be there in a few minutes, since it was on my way anyway.
When I got there, the alarm was buried in a network closet stacked with odds and ends. Boxes, a couple of decorative pieces, nothing that belonged in a server closet. I climbed over and around it all, doubting I’d fit if I were any bigger, until I found the panel and shut it off. She thanked me like I’d performed surgery. All I’d done was know where to look and be willing to climb over some stuff to get there.
What Good IT Support Looks Like
That’s most of what good IT support is. Knowing where things are and understanding how a business runs day-to-day well enough to spot what’s out of place before it turns into an emergency. None of that requires a special gift, just consistent attention, long before anyone calls in a panic.
The part nobody sees is most of the job. A firm with someone quietly monitoring their systems and catching a failing piece of hardware before it dies on a Friday afternoon rarely has a dramatic story to tell. A firm whose IT provider only shows up once something has already broken almost always does, and it’s usually an expensive one. Research from Information Technology Intelligence Consulting, which surveys businesses on exactly this question, has repeatedly found that a large share of small and mid-sized companies put the cost of even a single hour of unplanned downtime in the tens of thousands of dollars. Businesses that never feel that cost aren’t lucky. Someone was paying attention before there was a fire, occasionally a literal one.
Technology Is Just the Excuse
Part of the reason this looks like magic is that my industry does a poor job explaining what we do all day. We talk about firewalls and patch schedules like the details are the point. They rarely are, for the client anyway. The real point is that a law office doesn’t miss a filing deadline because someone moved a copier and forgot to mention it. The real point is that a property manager doesn’t lose an afternoon locked out of a shared drive during a lease signing. Technology is just the excuse. The job is understanding how a business runs and staying a step ahead of whatever might interrupt it.
So next time something at your office quietly works exactly the way it’s supposed to, the printer connects, the email doesn’t crash, resist the urge to call it luck. Ask your IT provider one question instead: what did you do this month that I never had to see? If they can answer that clearly, you’ve found your own jack fairy. If they can’t, you’re probably paying for emergencies instead of prevention, and that’s always the more expensive way to run a business.
Anthropic just published a blog post admitting that one of its Claude models escaped a supposedly sealed test environment and gained unauthorized access to three real companies. My inbox filled up within hours. Clients wanted to know if their AI was about to go rogue.
It isn’t. Read the actual report, and the story is a lot less Terminator and a lot more familiar: someone on the setup side left a door unlocked.
What Anthropic actually found
Anthropic reviewed 141,006 evaluation runs from its cybersecurity testing program, the kind of testing every serious AI lab runs before releasing a model. Out of that entire set, three incidents stood out. In each one, Claude was given a capture-the-flag challenge: find a piece of hidden information on a network and retrieve it, using whatever method works.
Claude was explicitly told that the test environment had no internet access. That statement was wrong. A misconfiguration between Anthropic and a third-party evaluation partner, Irregular, left the machines connected to the real internet. When Claude’s search for the flag led it to real systems, it had no reason to think they weren’t part of the simulation. So it treated them like part of the simulation, and in a handful of cases, it got in.
The techniques involved were not exotic. A weak password here, an exposed debug page there, a missing check on a package registry somewhere else. These are the same causes behind most breaches I’ve dealt with in 35 years of doing this work.
The tell: this was a setup failure, not a rebellion
The detail that matters most is the one getting the least attention in the panicked headlines. This was, in Anthropic’s own words, closer to an operational failure than a model behaving badly on purpose. The model was told a specific thing about its environment. That thing was false. It acted on false information, which is exactly what happens to humans every single day of the week.
There’s also a detail worth sitting with. The three affected companies hadn’t detected the activity themselves. Anthropic found it during an internal review and reached out to them. Their own AI told on itself before their security did.
We’ve seen this movie before, minus the AI
I’ve watched this exact pattern play out in traditional IT breaches for decades. When Kaseya, the platform that powers a huge chunk of the managed services industry, including ours, had a major security incident several years back, the story that circulated afterward was that an intern had made the mistake. Everyone in the industry I talked to at the time had the same reaction: an intern doesn’t have that kind of access unless someone above them set it up that way.
Breaches are rarely the result of some sophisticated actor doing something no one could have anticipated. They happen when a system is configured wrong, a permission is left too open, or a check that should have run didn’t. Anthropic’s incident report reads like every other post-mortem I’ve read in this industry, except that this time the thing exploiting the gap was a language model rather than a person with a laptop.
AI is a chainsaw, not a mind of its own
I tell clients this all the time: AI is as dangerous as a chainsaw. In the right hands, with the right protective equipment, it’s one of the most useful tools you can put in front of a team. Handed to someone in flip-flops with no guard on the blade, it will absolutely take a toe off. The tool didn’t do anything wrong in either case. It did exactly what it was pointed at.
Claude didn’t decide to attack three companies. It was told to find a flag, told the range was sealed, and given no boundary on how to look. When the boundary turned out to be fiction, it kept doing the job it was assigned to do. That’s not a machine developing intent. That’s a machine following instructions built on bad information, at a scale and speed no human could match, which is exactly why the setup around these tools matters more than ever, not less.
What this means if you’re running a business, not a research lab
You don’t have to be evaluating frontier models to have this exposure. If your firm has rolled out AI tools this year, and most professional services firms I work with have, ask yourself whether someone actually configured those tools correctly and wrote down how they’re allowed to be used. That’s the question that matters. Whether the AI itself can be trusted is a much smaller concern by comparison.
I’ve written five AI usage policies for clients in the last two weeks alone. None of them had an incident, but they had never written down what their AI tools are allowed to touch, who’s responsible for checking the output, and what happens when something goes wrong. That gap is where the next headline comes from, and it has nothing to do with the AI misbehaving.
If Anthropic, with a dedicated security team and a third-party evaluation partner, still had a misconfiguration slip through, it’s worth asking what’s sitting unchecked in your own environment right now. Reach out if you need help doing that.
Most professional services firms assume compliance standards apply to somebody else. Then a client sends a security questionnaire before signing a new engagement, or a cyber insurance renewal asks for documentation nobody in the office has seen before.
That is usually the first time compliance readiness for a small business stops being an abstract phrase and turns into a deadline. Accounting practices, law offices, and property management firms handle financial records, personal information, and sometimes payment data every day. That activity puts many of them within the scope of HIPAA, PCI DSS, or SOC 2 requirements, even though no one at the firm set out to become a regulated business.
These firms aren’t careless. Nobody explained which rules actually apply, what those rules require in practice, or where a firm this size should start.
Why Compliance Is Showing Up in More Conversations
Insurance carriers tightened their underwriting standards over the past few years. Cyber liability policies now ask pointed questions about multi-factor authentication, backup testing, and incident response plans before a carrier issues or renews coverage. A firm that can’t answer those questions in writing risks a higher premium or a denied claim.
Clients are asking the same questions. Banks, private equity firms, and larger corporate clients increasingly require a completed security questionnaire or a SOC 2 report before they hand a vendor sensitive data. A law firm handling a corporate client’s litigation, or an accounting firm managing a private equity portfolio company’s books, can lose the engagement over a missing document, not a missing capability.
Professional services firms have also become a bigger target than most owners realize. Ransomware groups shifted their attention toward legal, accounting, and consulting firms, which accounted for close to one in five ransomware attacks in a recent quarter, according to the ransomware recovery firm Coveware. Attackers know these firms hold client financial records, case files, and personal data, and that most run leaner security than hospitals or banks do.
None of this means a fifty-person accounting firm needs a compliance department. It means understanding which standards apply to the business and building a short list of documented practices that satisfy most of what insurers, clients, and auditors ask for.
What HIPAA, PCI, and SOC 2 Actually Cover
HIPAA governs protected health information and applies to healthcare providers, as well as vendors and business partners that handle health data on their behalf. A property management firm running a medical office building, or an accounting practice with healthcare clients who share patient billing data for reconciliation, can find HIPAA obligations attached to work that never looked medical on the surface.
PCI DSS applies to any business that processes, stores, or transmits credit card data. Property management firms collecting rent through an online portal, and law firms accepting card payments for retainers, both fall under PCI requirements the moment a card number touches their systems, even indirectly through a payment processor.
SOC 2 is different from the other two. It isn’t a law. It’s an audit standard that proves an organization has real controls around the security, availability, and confidentiality of data. Firms don’t usually pursue SOC 2 because a regulator demands it. They pursue it because a client, a bank, or an insurer asked for the report, and without it, the deal stalls.
This plays out constantly: an accounting firm picks up outsourced payroll work for a physician client and signs on to keep handling billing reconciliation, then realizes months later that arrangement pulled HIPAA obligations into scope. That kind of realization arrives late more often than it should, usually attached to a deadline.
How to Figure Out Which Ones Apply to You
Start with three questions instead of the full text of each standard.
- Does the firm handle protected health information, directly or through a client relationship? If yes, HIPAA obligations are worth reviewing with someone who understands both the technology and the legal exposure.
- Does the firm accept, store, or transmit credit card numbers in any form, including through a client portal or a property management platform? If yes, PCI DSS requirements apply, even at a small scale.
- Has a client, bank, or insurer ever asked for a completed security questionnaire or a SOC 2 report? If this keeps happening, formal readiness work will save more time than answering the same fifteen-page questionnaire from scratch every quarter.
Most firms find they touch at least one of these standards without ever intending to.
What Readiness Actually Looks Like
Compliance readiness for a fifty- to one hundred fifty-person professional services firm rarely means a five-hundred-page policy binder. It means having documented, working answers to the questions insurers and clients keep asking: multi-factor authentication on every account, tested backups, a written incident response plan, defined access controls, and a basic record of how vendors who touch client data are vetted.
Firms that build these practices once tend to stop dreading every renewal and every new client questionnaire, because the answers already exist. The alternative, scrambling to document controls under deadline pressure, costs more time and usually produces weaker documentation than doing the work upfront.
If you want a structured way to see where your firm stands, our Cyber Liability Insurance Readiness Checklist walks through the eight security categories insurers and compliance frameworks care about most, and shows you exactly where professional services firms typically fall short. Download it, work through it with your team, and you’ll know within an hour which of these standards deserve real attention.