
I have a standing rant about password security for small businesses. If you have sat in a meeting with me for more than twenty minutes, you have probably heard some version of it. Denmark just gave me the best opening line I’ve had in years.
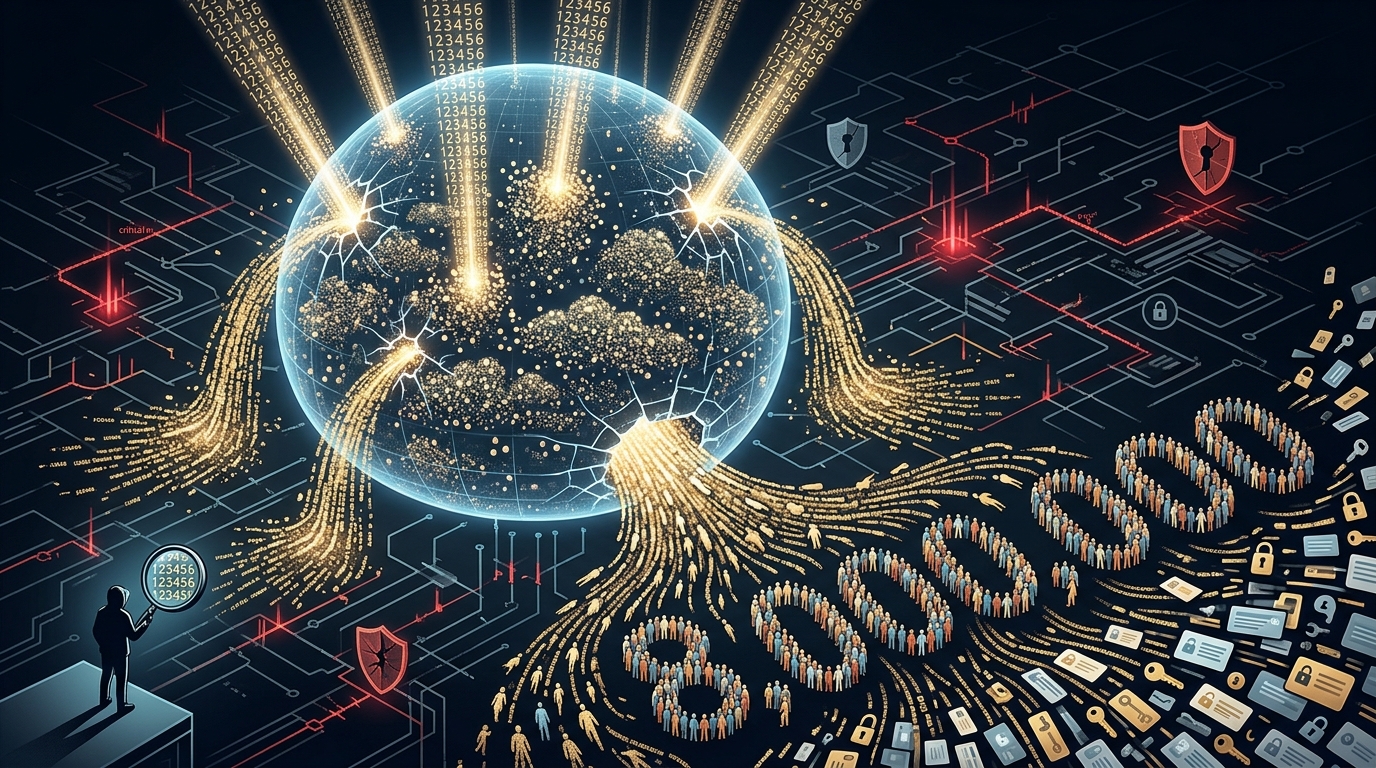
Earlier this month, the Danish government confirmed that someone got into its Central Register of Persons, the national database that holds the core identity record for nearly every resident. The attacker accessed information on 8.8 million people. The person claiming responsibility says they got in through an account at a small IT company with legitimate access to the registry, and that account’s password was “123456.” Danish newspaper Politiken reported that at least three of the company’s accounts used that same password, including an administrator account.
How a six-digit password reached 8.8 million records
The details are worth a minute of your time. According to documents reported by Danish broadcaster TV 2, the attacker first logged in on September 10 and ran roughly 14 million automated searches over the next ten days. Nobody noticed until October 2.
I keep coming back to how they finally caught it. No security tool flagged it. A staffer at the ministry noticed an invoice showing unusually high activity from the vendor’s account. Someone read a bill.
That vendor, a company called Pays ApS, was authorized to use the registry to validate business customers’ records. Its managing director has confirmed the company’s access was exploited. A small firm held the key to something enormous, and it protected that key with the first six digits on the keyboard.
If you run a professional services firm, that arrangement should feel uncomfortably familiar.
Convenience wins the first round almost every time
I don’t think anyone at that company is stupid. I think someone set up a handful of accounts, needed several people to get into them, picked something everyone could remember, and told themselves they would fix it later. Later never came. I see the same pattern in firms of 50 people and firms of 150.
Humans pick convenience over security by default. Security takes effort, and effort loses to a filing deadline every single time. One weak password is a mistake. Three accounts sharing it, one of them with administrator rights, is a habit, and habits are exactly what attackers count on.
The shared admin password usually exists because sharing access is a real problem. The seasonal hire needs access to the client portal. The office manager needs access to the vendor account while the partner is on vacation. Nobody wants to be the bottleneck for a two-factor code at 8 p.m., so the fix has to make sharing safe. Pretending people won’t share has never worked.
Your vendors hold keys to your data too.
Denmark’s breach did not start inside the government. It started at a vendor. That is the part I want every CFO and managing partner to sit with for a minute.
Verizon’s 2025 Data Breach Investigations Report found that third-party involvement in breaches doubled to 30 percent, while credential abuse remained a leading way attackers got in at 22 percent. Your firm’s data does not just live on your own servers. It lives with your practice management software, your document portal, your payroll provider, and, yes, your IT company. That includes us.
Every one of those relationships involves accounts that someone, somewhere, protects with a password. You are allowed to ask how. Good vendors will answer without getting defensive. A vendor that gets cagey about it has told you something important.
What we do about shared passwords at C2
We have the same sharing problem every firm has, multiplied by every client account we manage. Our answer is a password manager. We use Keeper, which lets us share credentials across the team and attach the second factor to them. In practice, a technician can access the account they need without me texting a password, and without anyone chasing me for a two-factor code.
Every admin account gets its own unique password and multifactor authentication. When someone leaves, their access leaves with them, and we never have to wonder which sticky note they saw. We also want to hear about strange activity long before an invoice arrives. Fourteen million searches should set off an alarm somewhere other than accounts payable.
None of this is exotic. It is the same tooling large companies use, at a price that makes sense for a 75-person firm. Small businesses deserve that, and frankly, so do the people whose records they hold.
One question to ask this week
Send one email to your IT provider and one to the vendor that holds your most sensitive client data. Ask them this: “Does any account with access to our data share a password with another account?”
Suppose the answer comes back fast and clear, great. If it takes a week and a pile of meetings, you have your answer.